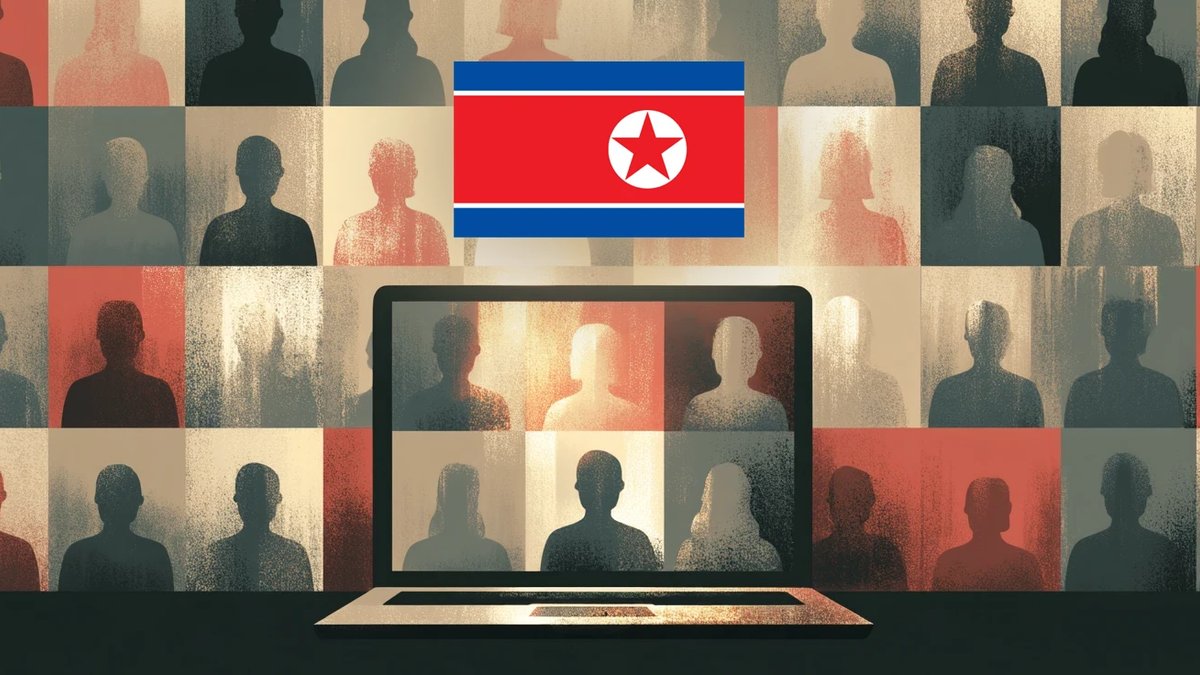
North Korean state hackers have stolen over $400 million in cryptocurrency in the past 18 months through a fake Zoom and Teams call scheme. The FBI calls this scheme FaceStealer, which involves using stolen webcam footage of earlier victims to lure new targets.
The hackers have seized more than 900 recordings and warned crypto and web3 workers and open-source maintainers about the scheme on November 12. Each successful call infects the target and records them, making each new victim a familiar face on the next call.
The scheme works by hackers taking over earlier victims’ social media and messaging accounts, reading their chat histories, and messaging their contacts about catching up or an investment. A Calendly invite sets the time, and the meeting link arrives shortly before the call, pointing to a lookalike domain.
Once in the call, the hackers play the contact’s recorded video, often next to clips of other “participants.” A chat message then says the others can’t hear the target and walks them through an update, a script, or a command to paste into their terminal.
Following the hackers’ steps installs a cookie harvester, keyloggers, a screen capturer, and a backdoor. The target’s webcam has been recording since they clicked the link. They are in no hurry, often waiting months or over a year for wallet balances to grow before emptying them.
The FBI advises leaving the webcam off until the target can see, hear, and talk with the person who invited them. They should join through the official Zoom or Teams app with an invite code and confirm the meeting through a second channel.
However, stolen footage of real victims still makes up the overwhelming share of the scheme.
To protect themselves, individuals should keep only small amounts in browser extension wallets and store no recovery phrases or private keys on their devices. If they suspect a compromise, they should create a new wallet on a clean device and move everything into it.
The FBI has seen other attempts against maintainers on npm and Rust crates, and the group got the maintainer of a major open-source JavaScript library into a fake Teams call earlier this year. The attack was caught and stopped quickly.



Leave a Reply